Advanced-etl-processor
Send Syslog Message Dynamic Action
About
Syslog is a standard way for applications, servers, and network devices to send log messages to a central collector. A message can include the timestamp, source application, severity, and event details.
SIEM stands for Security Information and Event Management. It’s software that collects events from multiple systems, searches and correlates them, and raises alerts about suspicious activity. A SIEM can receive logs through syslog and other methods.
Metadata tab
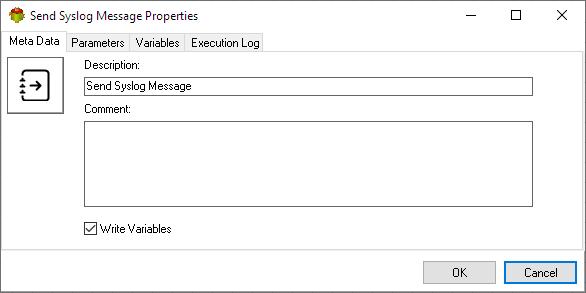
- The Write Variables option ensures that the “Package Action” logs the variable values into the “Action vars before log file” before the action is executed and logs the updated variable values into the “Action vars after log file” after the action completes.
- This option is typically used for debugging and is not recommended in a production environment.
- It can be globally disabled through the options dialog .
Parameters tab
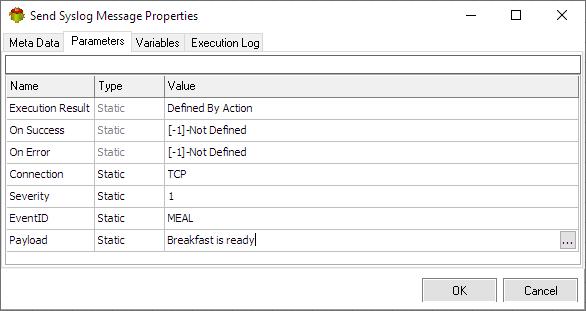
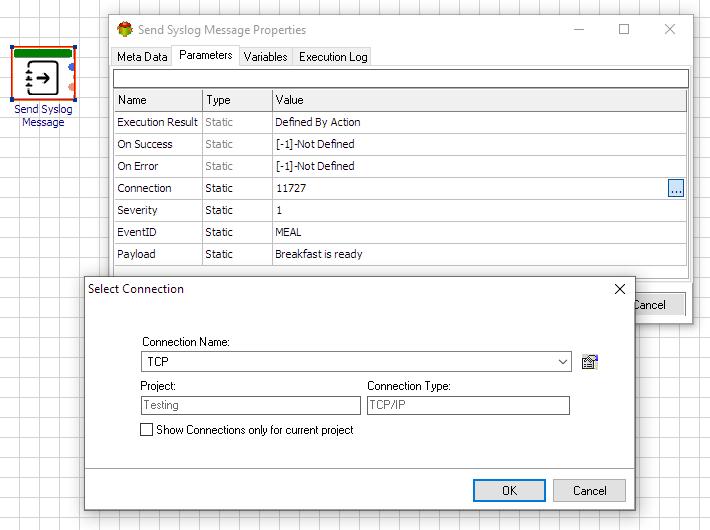
Selecting Connection
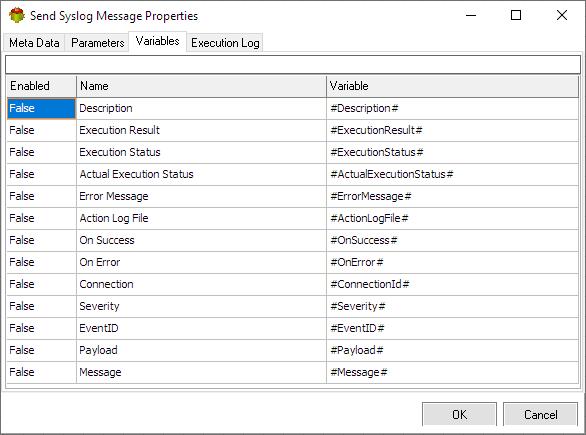
Variables tab
The Variables tab defines which variables are updated during the execution of the action.
Execution log tab
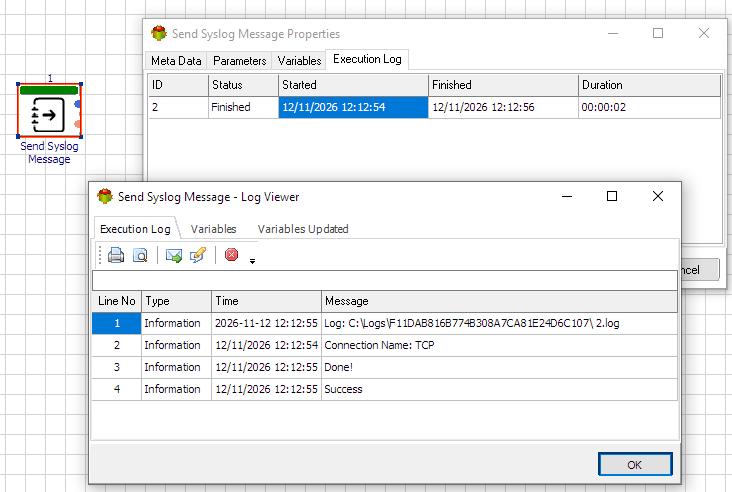
The Execution Log tab is populated after the action has been executed. Double-click a row to view the detailed execution log.
Example Calculated SysLog Message
Pascal
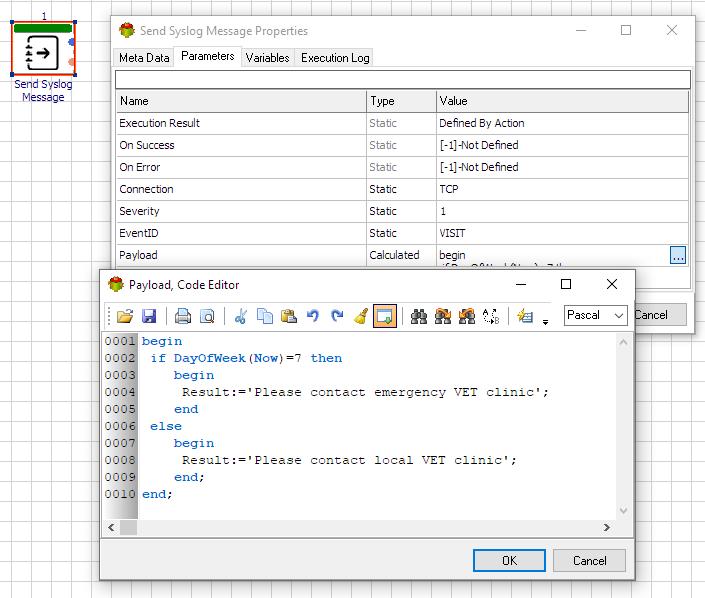
begin
 if DayOfWeek(Now)=7 then
    begin
     Result:='Please contact emergency VET clinic';
    end
 else
    begin
     Result:='Please contact local VET clinic';
    end;
end;
Python
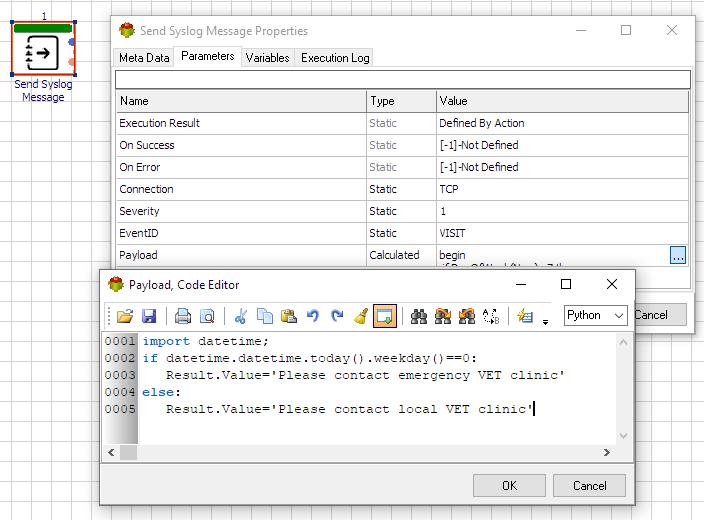
import datetime;
if datetime.datetime.today().weekday()==0:
   Result.Value='Please contact emergency VET clinic'
else:
   Result.Value='Please contact local VET clinic'
Useful Links
For more technologies supported by our ETL Software see Advanced ETL Processor Versions
Confused? Ask question on our ETL Forum